Blog
Writing about AI — how it works, where it helps, and what we learn building with it.
Latest posts
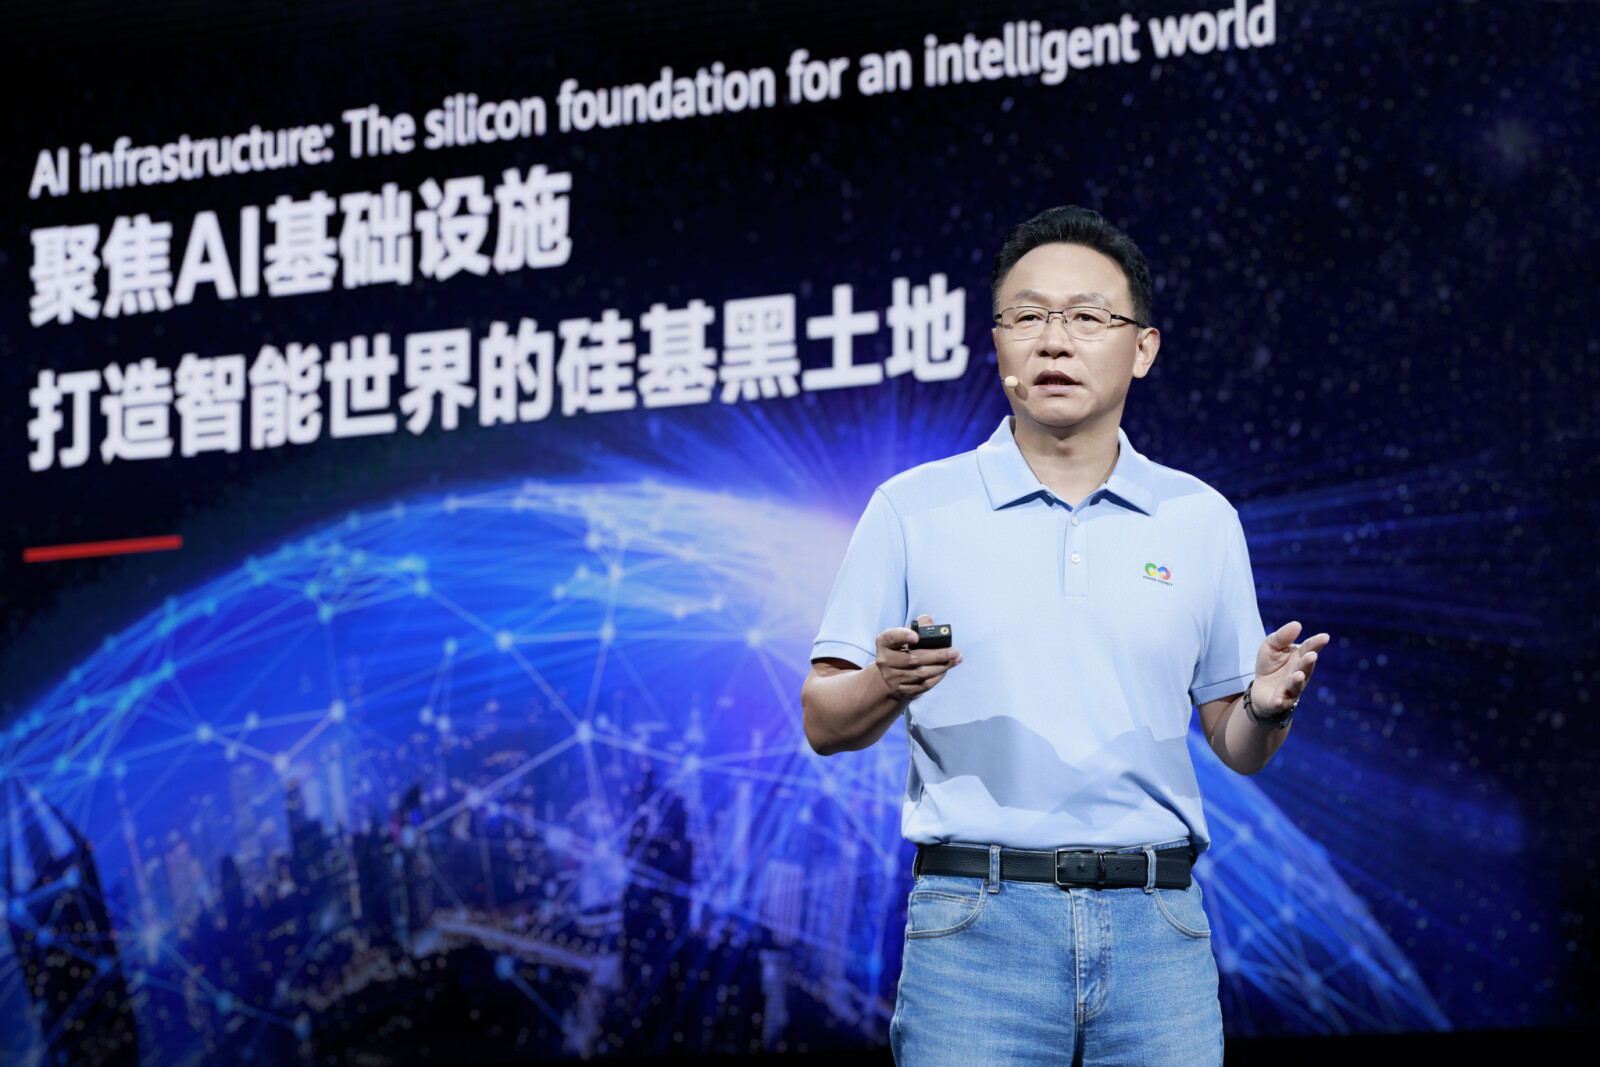 Huawei Moved Its Next AI Chip Up Nine Months. The Part Worth Reading Twice Was About LightAt Huawei Connect 2026 the company pulled the Ascend 960DT forward to Q1 2027, but the accelerator date is a supply signal, not a silicon one. The real announcement was Hi-ONE, a near-packaged-optics interconnect Huawei says is the first ready for volume manufacture.Engineering
 Cisco's Identity Engine Decides Who Gets On the Network. One Unauthenticated Request Skips the QuestionCVE-2026-76460 is a CVSS 10.0 authentication bypass in Cisco Identity Services Engine, already exploited in the wild, with no workaround and a three-day CISA deadline. Root on ISE means owning the rules that decide what everyone else can reach — and the logs that would show it.Security
 A Hijacked Coding Assistant Seeded a Worm Across 100 Repositories. Mandiant Says the Model Was Not the FlawGoogle's Mandiant has published a casebook of real 2026 AI incidents, including a hijacked coding-assistant session that spread the Shai-Hulud worm across about 100 internal repositories. The pattern running through it is that the agent has become a privileged identity, and is being attacked like one.Security
 CISA's ScreenConnect Deadline Expired Two Days Ago. A Thousand Instances Are Still ExposedCVE-2026-84869 is a 9.9-rated authorization failure in ConnectWise ScreenConnect that attackers used to spread across connected endpoints from late August. The federal patching deadline has passed and Shadowserver still counts over a thousand exposed instances.Security
 Europe's Under-13 Ban Got the Headline. The Kids Act Also Puts AI Companions Inside ItVon der Leyen announced the age limits in Strasbourg on Wednesday; the Commission presents the Kids Act on Thursday. The numbers are negotiable — the architecture underneath, which pushes age checks to the app store and pulls AI companions into child-safety law, is not.Artificial intelligence
 The Pixel Zero-Day Under Attack Is Not a Memory Bug. That Is the Uncomfortable PartGoogle's September Pixel bulletin fixes CVE-2026-58704, a cellular modem permission bypass the company says may be under limited, targeted exploitation. It is rated High, it appears only in the Pixel-specific bulletin, and it is a logic error — the one class Google's Rust baseband work does not touch.Security
 Google Won the Voice Benchmark by 1.1 Points. It Undercut the Price by Seven TimesGemini 3.8 Live Extended Thinking takes the top spot on Artificial Analysis' speech quality index by 1.1 points over OpenAI's GPT-Live-1 Astra. The interesting number is the price: roughly a seventh of what the model it beat costs per hour.Artificial intelligence
 Shanghai AI Lab Did Not Train Its Frontier Model. It Post-Trained Z.ai'sShanghai AI Laboratory released Atria Dawn Preview, a 744B agentic mixture-of-experts model, under an MIT licence — built on Z.ai's GLM-5.2 base rather than one of its own. The division of labour is the story, and export controls do not reach the layer it happened in.Artificial intelligence
 LiteSpeed Patched a Root Escape on Shared Hosting. It Did Not Give It a NumberLiteSpeed Web Server Enterprise 6.3.7 quietly fixes a flaw that lets one hosting account reach root on a shared server, breaking the isolation the whole model depends on. There is no CVE, no severity score, and no word on exploitation — cPanel had to issue the warning.Security